


This brief highlights significant threats to US homeland security posed by China, Russia, Iran, and North Korea observed in October 2026.
Executive Summary:
Observed Threats - Current activity that poses a direct risk to US homeland security
The FBI arrested a California real estate agent accused of spying for China on the US home of the son of Taiwan’s president.
A joint cyber advisory by the US and allies labeled Chinese government-linked cybersecurity company Integrity Technology a key facilitator of malicious cyber attacks.
US law enforcement disrupted multiple North Korean remote IT work schemes involving American intermediaries.
The New York Times reported that Nvidia CEO Jensen Huang developed a close relationship with a suspected Chinese spy allegedly involved in the smuggling of advanced chips to China.
Sophisticated AI-generated disinformation targeting multiple Democratic Senate candidates was attributed to Russian influence operation “Storm-1516”.
Horizon Threats - International activity that may pose a future risk to US homeland security
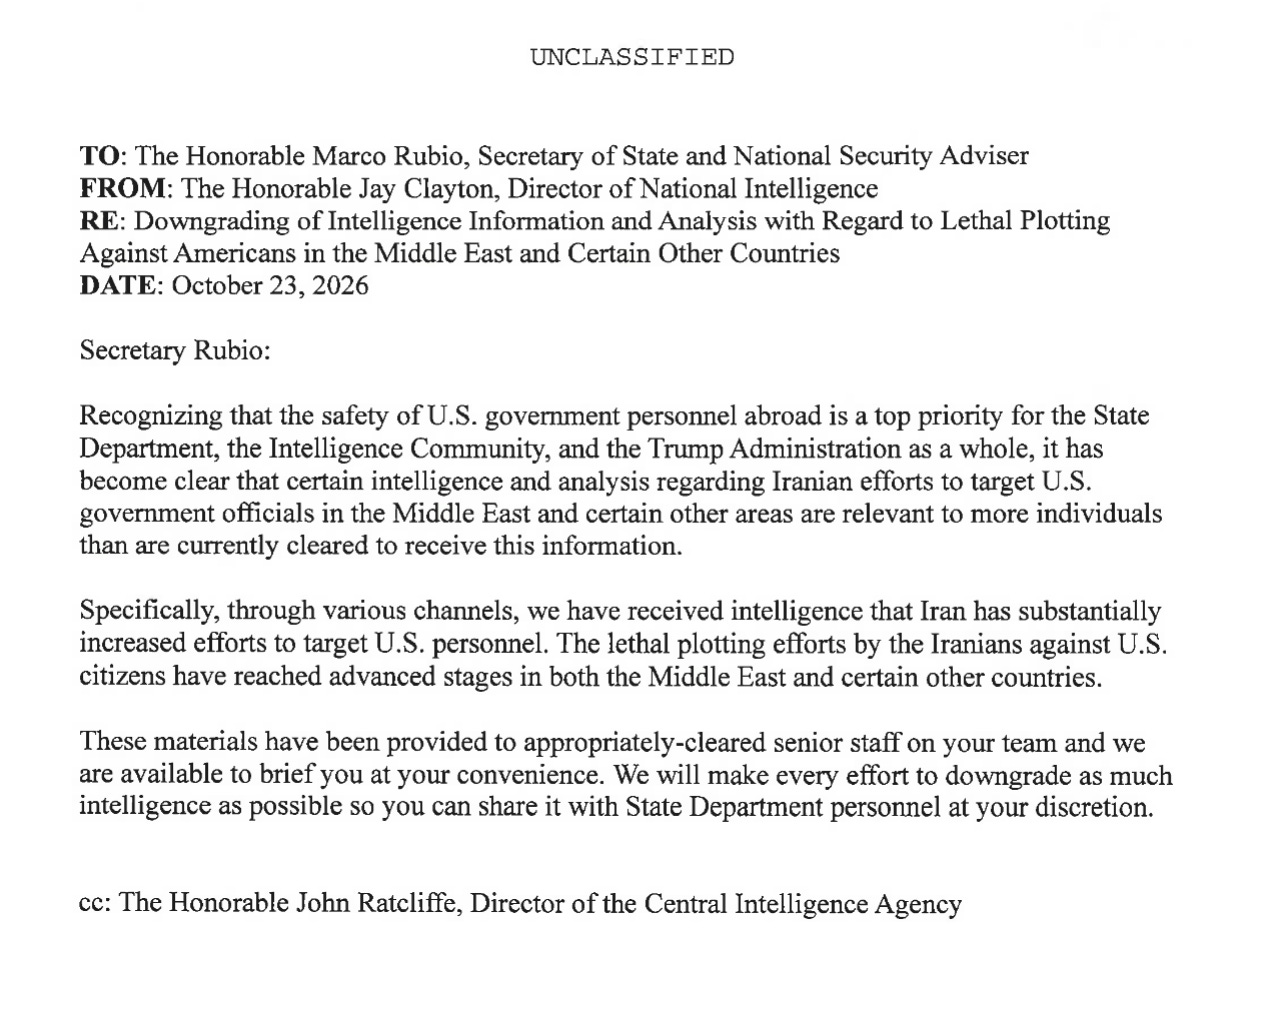
The Director of National Intelligence warned that Iranian plots to attack Americans abroad were in “advanced stages”.
The Canadian Broadcasting Corporation found evidence of Iranian involvement in 12 shootings targeting Jewish communities, Iranian dissidents, and the US Consulate in Toronto.
OBSERVED THREATS
Current activity that poses a direct risk to US homeland security
1. CALIFORNIA REAL ESTATE AGENT ARRESTED FOR SPYING ON THE FAMILY OF TAIWAN’S PRESIDENT FOR CHINA
On October 5, 2026, the US Department of Justice announced the arrest of Wanying “Heather” Zhang on charges of serving as an illegal agent of the Chinese government. Zhang was allegedly tasked by a Chinese official in June 2025 with surveilling the family of a high-ranking Taiwanese official in the US. In September 2025, Zhang and an accomplice, Fatai Miao, collected and transmitted video and photos of the target’s Seattle residence and vehicles to their handler in China. The target has been revealed as the son of current Taiwanese President Lai Ching-te.
Zhang was arrested by the Federal Bureau of Investigation (FBI) on October 4, 2026, a day before charges were publicly announced, while trying to board a flight to China at Los Angeles International Airport.
Additional Information:
Reporting by CBS News has found that Zhang has ties with a notorious multibillion dollar Chinese fraud ring known as the “Prince Group”. The group has targeted Americans in romance scams and other fraud schemes run out of 10 different forced labor camps in Cambodia.
Zhang’s arrest follows other notable recent cases of Chinese transnational repression in the Los Angeles area. In May 2026, Eileen Wang, the then-mayor of Arcadia, a small city in Los Angeles County, was arrested and pleaded guilty to operating as an illegal foreign agent of China. Her arrest was preceded by the conviction of two co-conspirators, Yaoning “Mike” Sun and Chen Jun (aka John Chen). All three worked with intelligence officers stationed at the Chinese Consulate in Los Angeles to spread Chinese propaganda as well as surveil and intimidate overseas Chinese populations living in the area. Sun and Chen specifically engaged in efforts to target individuals perceived as sympathetic to Taiwan. The pair notably sent photos to the LA Consulate of attendees at a pro-Taiwan rally in April 2023 during the visit of then-Taiwanese President Tsai Ing-wen to Southern California.
2. NEW JOINT ADVISORY IDENTIFIES GOVERNMENT-LINKED CHINESE COMPANY AS KEY FACILITATOR OF MALICIOUS CYBER OPERATIONS
On October 8, 2026, the FBI, National Security Agency (NSA), and Cybersecurity and Infrastructure Security Agency (CISA) issued a joint advisory (AA26-281A) with government cyber agencies from Australia, Canada, Japan, New Zealand, Spain, and the UK that named Chinese company Integrity Technology Group a key enabler of malicious cyber activity emanating from China. The advisory describes Integrity Technology Group, which has ties to the Chinese government, as a sort of support organization that builds and acquires the codebases, software, and web infrastructure that are used by Chinese threat actors to conduct malicious cyber activities. Chinese threat actors that may be involved with Integrity Technology Group include “Flax Typhoon”, “Ethereal Panda”, and “Red Juliett”.
One of the most concerning of Integrity Technology Group’s operations outlined in the advisory is the development of a database containing a trove of stolen emails from previous data thefts that is provided as an intelligence product to third-party subscribers.
The threat actors maintain a custom web application that provides third-party access to stolen email content. Users of this application can pass specific arguments in URLs to see email content for specific accounts.
Additional Information:
Integrity Technology Group was sanctioned by the US Department of the Treasury in January 2025 over its support for Chinese cyber espionage group Flax Typhoon. According to the Treasury Department, between the middle of 2022 and the end of 2023, Flax Typhoon used Integrity Technology Group’s IT infrastructure to launch its intrusions into private networks.
In a September 2024 keynote address at the Aspen Cyber Summit, then-FBI Director Christopher Wray noted that Integrity Technology Group’s chairman publicly admitted to collecting intelligence for the Chinese security services.
3. MULTIPLE NORTH KOREAN REMOTE WORK SCHEMES INVOLVING AMERICAN AGENTS DISRUPTED
Laptop Farms Linked to North Korean Remote Work Scheme Busted in Texas
On October 13, 2026, the US Department of Justice announced that it arrested two Americans1 and seized 187 computers at a series of laptop farms in Texas associated with North Korean remote IT work schemes. The busts resulted from a sweeping FBI operation, “Operation Lonestar Roundup,” that searched over 40 homes across the state between September 21 and 25, 2026. The operation also resulted in the 12 additional indictments, including 10 Chinese nationals living in China2 as well as two unidentified individuals.
According to the Department of Justice, the scheme targeted 70 US companies in the “health care, communications, cyber support, retail, and manufacturing sectors” in 17 states and Washington, DC, and raised more than $3 million for the North Korean regime.
Virginia Defense Contractor Pleads Guilty to Assisting North Korean Remote Workers
On October 28, 2026, John Allen Kurrle Jr., 62, of Gainesville, Virginia, pleaded guilty to conspiracy to commit wire fraud in a plot to help North Korean remote workers obtain positions at US companies. According to the Department of Justice, Kurrle, a Top Secret security clearance holding employee of an unnamed defense contractor, knowingly allowed North Korean operatives to use his identity and that of another person to obtain employment offers from nine companies in exchange for payments. Companies targeted in the scheme included government contractors. Kurrle further used laptops provided by the targeted companies to enable remote access for North Korean actors.
Additional Information:
An October 13, 2026, Public Service Announcement by the FBI (Alert Number: I-101326-PSA) warns that North Korea is increasingly recruiting American agents to facilitate its schemes by running laptop farms and even intimidating US targets.
Recently, the FBI has observed North Korean ITWs use threats of physical violence to demand payments and compel others to take action in support of their scheme. Following termination, ITWs have made death threats against former managers and their families to collect additional payments.
ITWs have threatened to release a victim’s sensitive corporate data or publicly post proprietary information unless they received large lump sum payments. ITWs have also threatened victim companies with reputational harm and posted negative information to force further payouts.
ITWs have hired U.S.-based facilitators to appear in-person at victim companies or at the residences of laptop farm operators for intimidation. Facilitators paid by ITWs have also made in-person threats against companies that removed ITW-related accounts.
4. SUSPECTED CHINESE SPY DEVELOPED A CLOSE RELATIONSHIP WITH NVIDIA CEO JENSEN HUANG
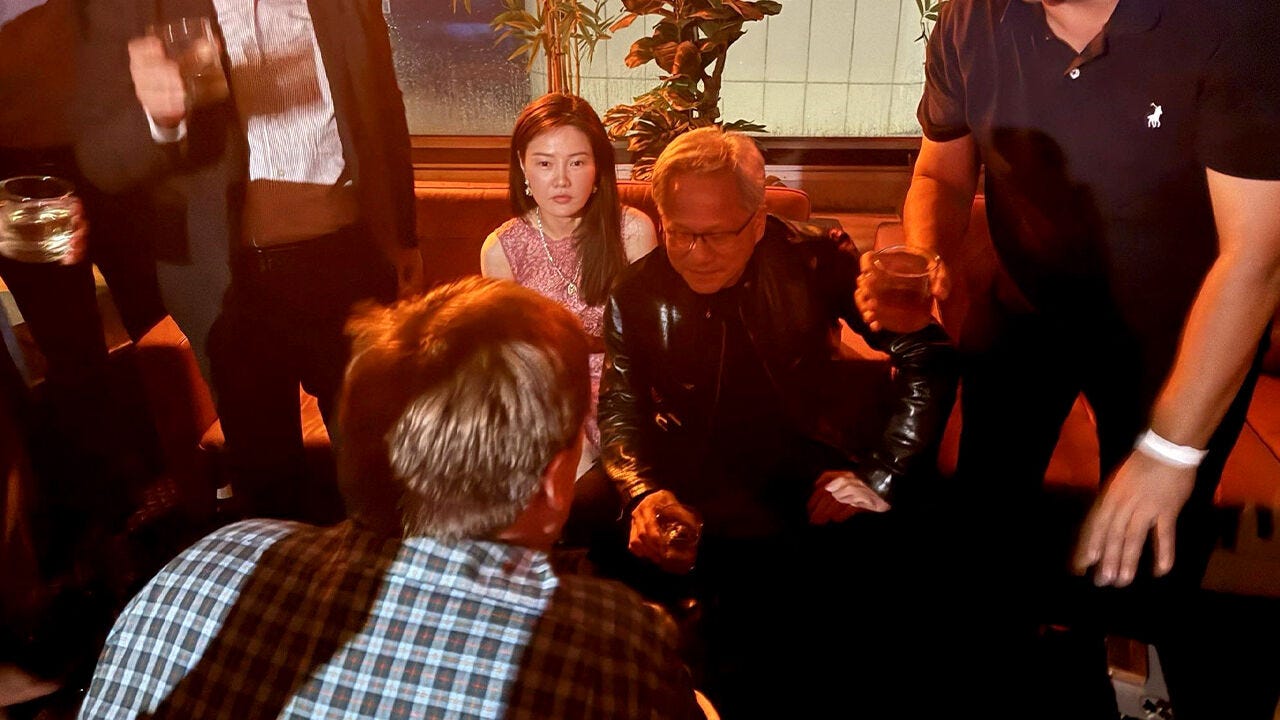
On October 29, 2026, The New York Times reported that Nvidia CEO Jensen Huang has developed a “close” relationship with Alice Huang (Huang Le), a senior executive at Singaporean AI firm Megaspeed, who US intelligence officials also believe has close ties with Chinese intelligence. US intelligence officials have been monitoring Jensen Huang’s ties with Alice Huang for over a year and at one point issued a warning to President Donald Trump over Alice’s ties to Beijing.
The relationship between the two unrelated Huangs is of particular concern as Megaspeed is a customer of Nvidia’s advanced AI chips and is suspected of illegally transshipping chips to China. An earlier New York Times investigative report released on October 9, 2025, found evidence that Megaspeed, under Alice Huang’s leadership, helped ship $2 billion worth of advanced AI chips to buyers in China in 2024 in violation of US export controls.
Additional Information:
On October 14, 2025, Senator Tom Cotton issued a public letter to Secretary of Commerce Howard Lutnick requesting an investigation into Megaspeed, accusing the organization of serving as a spin-off of 7-Road, a cloud computing provider for the Chinese government.
Reporting does not suggest Jensen Huang was aware that Alice Huang is a suspected spy. The government may not have informed him of its suspicions to avoid tipping off Alice Huang to ongoing surveillance.
5. RUSSIAN INFLUENCE OPERATION STORM-1516 TARGETED DEMOCRATIC CANDIDATES IN KEY SENATE RACES
An October 30, 2026, PolitiFact report found that a series of AI-generated videos targeting Democratic candidates in several competitive races appeared to show hallmarks of being generated by Russian influence operation Storm-1516. The videos specifically targeted Texas Senate candidate James Talarico and Ohio Senate candidate Sherrod Brown.
A video distributed on X on October 20, 2026, impersonating a real former student of James Talarico falsely accused the Texas candidate of sexual assault.3 Digital investigations organization Graphika assessed the video to be the work of Storm-1516.
A video distributed on X on October 26, 2026, depicting a Cleveland 19 News broadcast falsely reported that multiple staffers from Ohio candidate Sherrod Brown’s campaign accused him of sexual assault. NewsGuard, a digital media investigations organization, attributed the video to Storm-1516.
Maine Senate candidate Troy Jackson is also believed to be a target of Storm-1516 operations according to NewsGuard.
Additional Information:
Storm-1516 previously spread disinformation targeting the Harris-Walz campaign in the lead up to the 2024 presidential election. Microsoft Threat Intelligence described the operation as follows:
In late August and early September, Storm-1516 produced and disseminated two inauthentic videos designed to discredit Harris and stoke controversy around her campaign. The first video depicts an attack by alleged Harris supporters on what the video’s amplifiers claim is a Trump rally attendee. Storm-1516 intended this video, which received millions of views, to inflame political divides by stirring racial and political tensions. The second video used an on-screen actor to fabricate false claims that Harris paralyzed a girl in a 2011 hit-and-run accident. Storm-1516, following its tried-and-true method outlined in Election Report #3, laundered this video through a website masquerading as a local San Francisco media outlet—which outlet was only created days beforehand.
Since 2024, Storm-1516 has conducted disinformation operations targeting multiple European elections, notably in France, Germany, and Hungary. As part of the campaigns, the group established convincing fake websites of reputable European news organizations such as Euronews and the BBC to launder information along with fake bylines of real journalists.
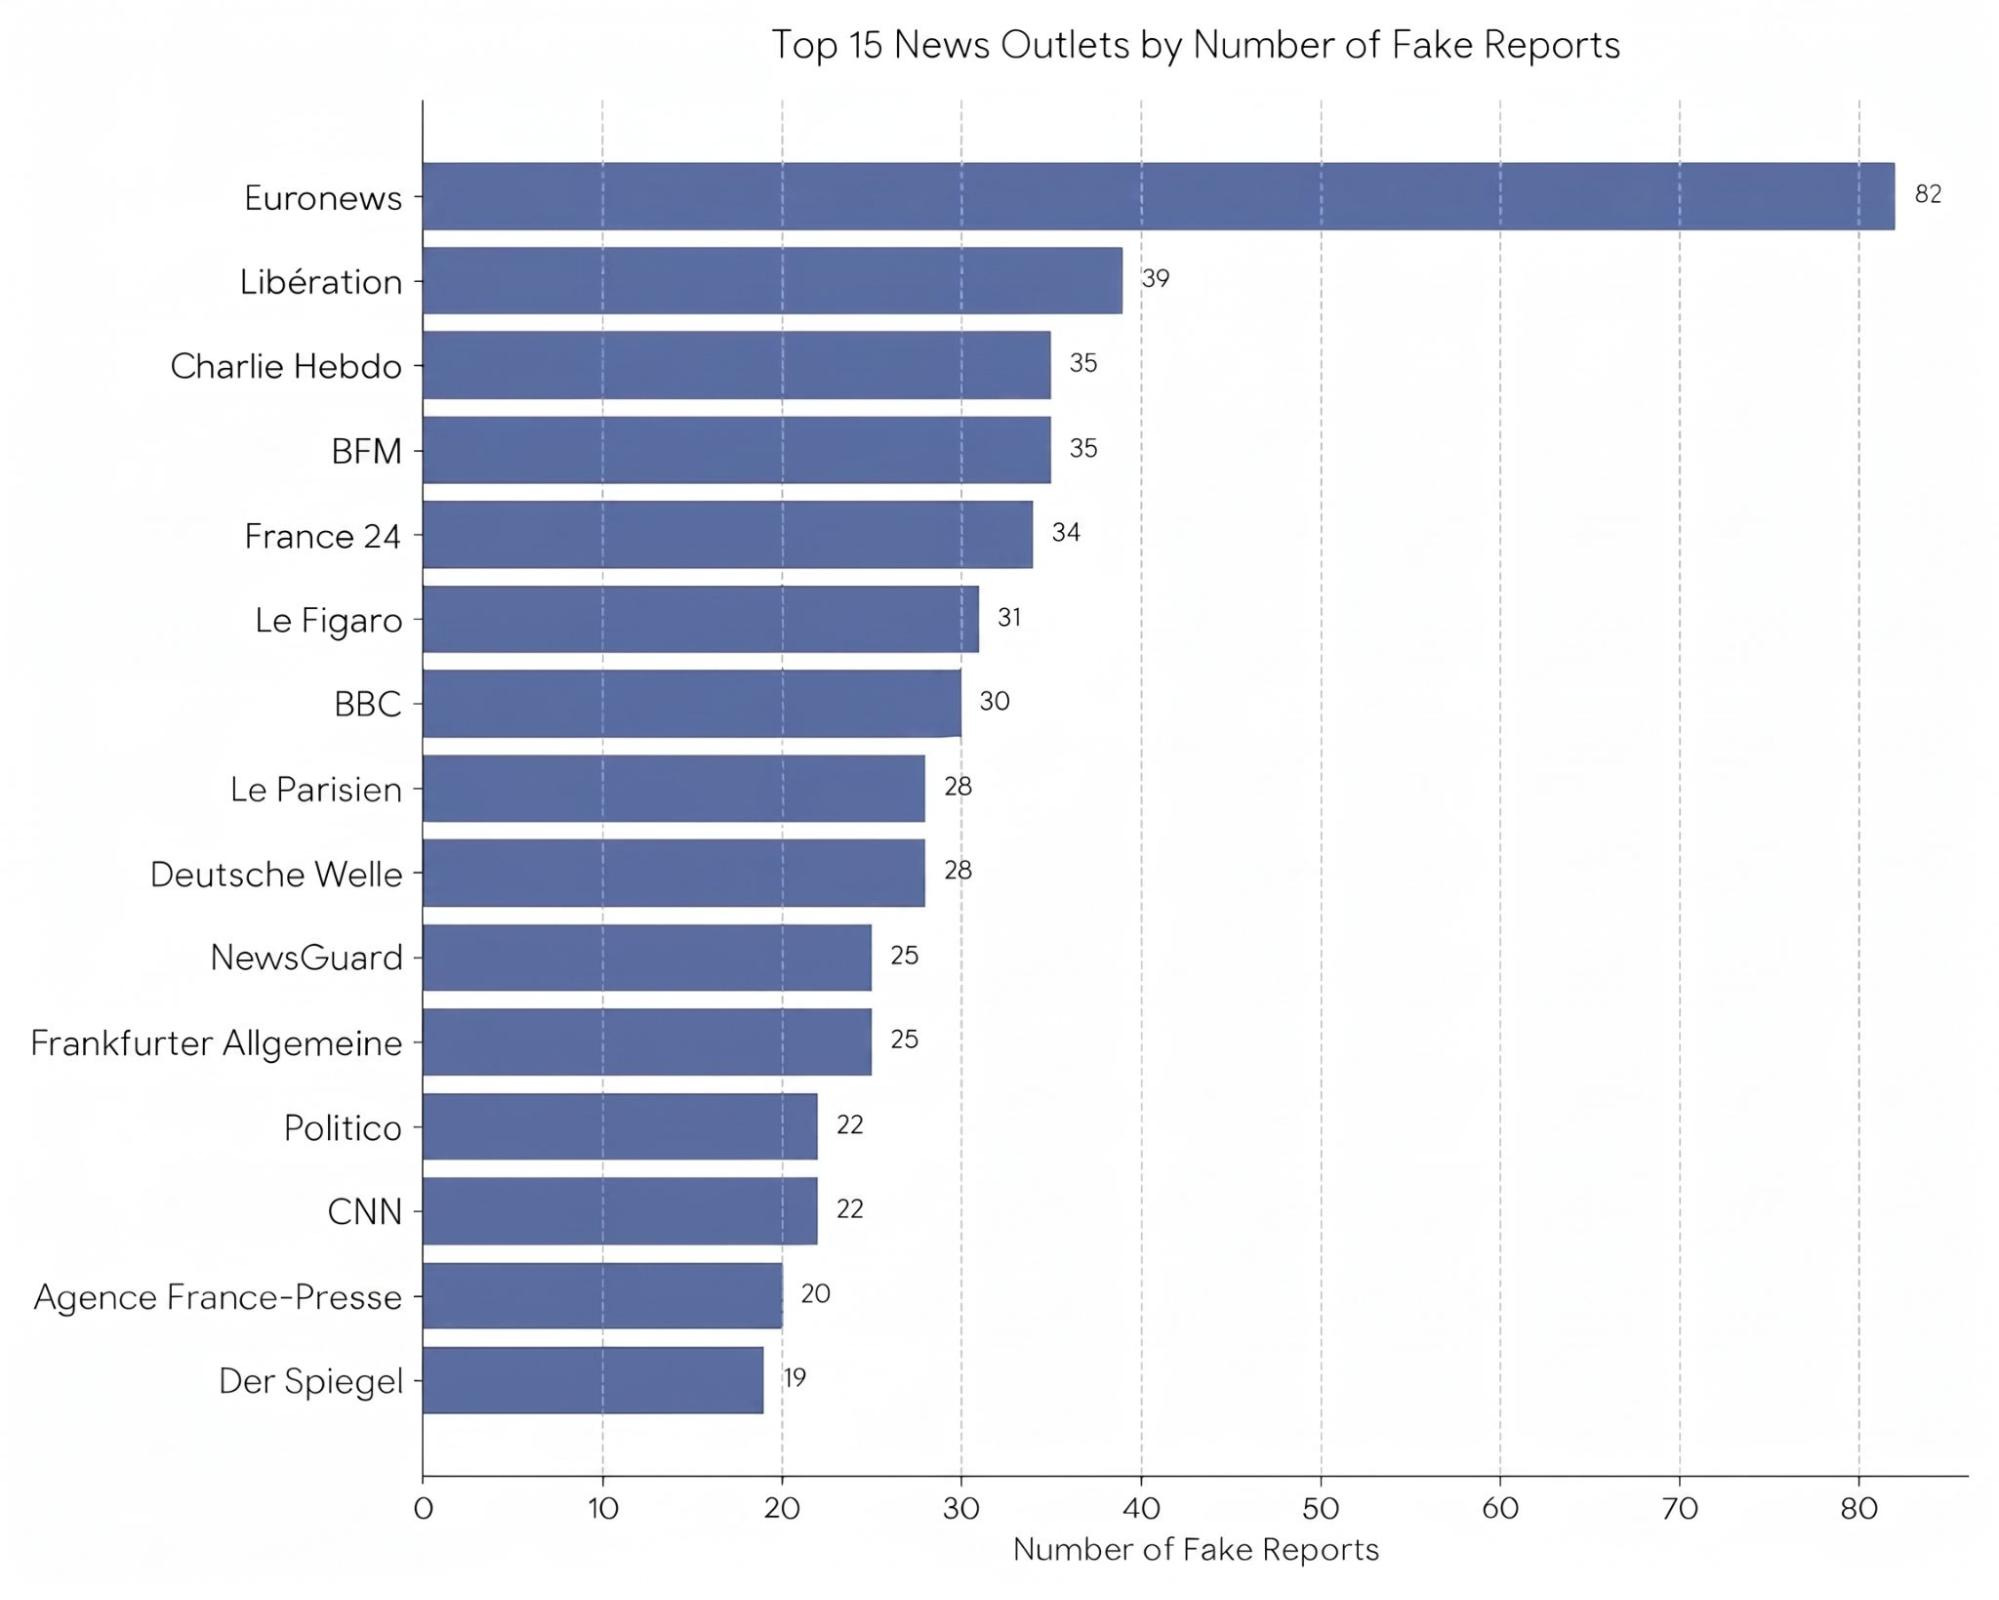
NewsGuard has found that since Russia’s 2022 full-scale invasion of Ukraine, Storm-1516 has produced at least 906 fake news reports impersonating 163 legitimate media organizations. According to NewsGuard:
The media brands targeted range from big names such as the BBC, Politico, Bloomberg News, and Euronews, to smaller titles such as Ukrainian news site The Kyiv Independent, U.K. regional newspaper The Yorkshire Post, and French regional newspaper La Montagne. In every case, the Russian campaigns hijack the brands’ logos and layouts, sometimes creating a new site using a URL similar to the authentic one, making it difficult for the typical user to discern that it is counterfeit. The stories often include invented quotes from actual subject experts.
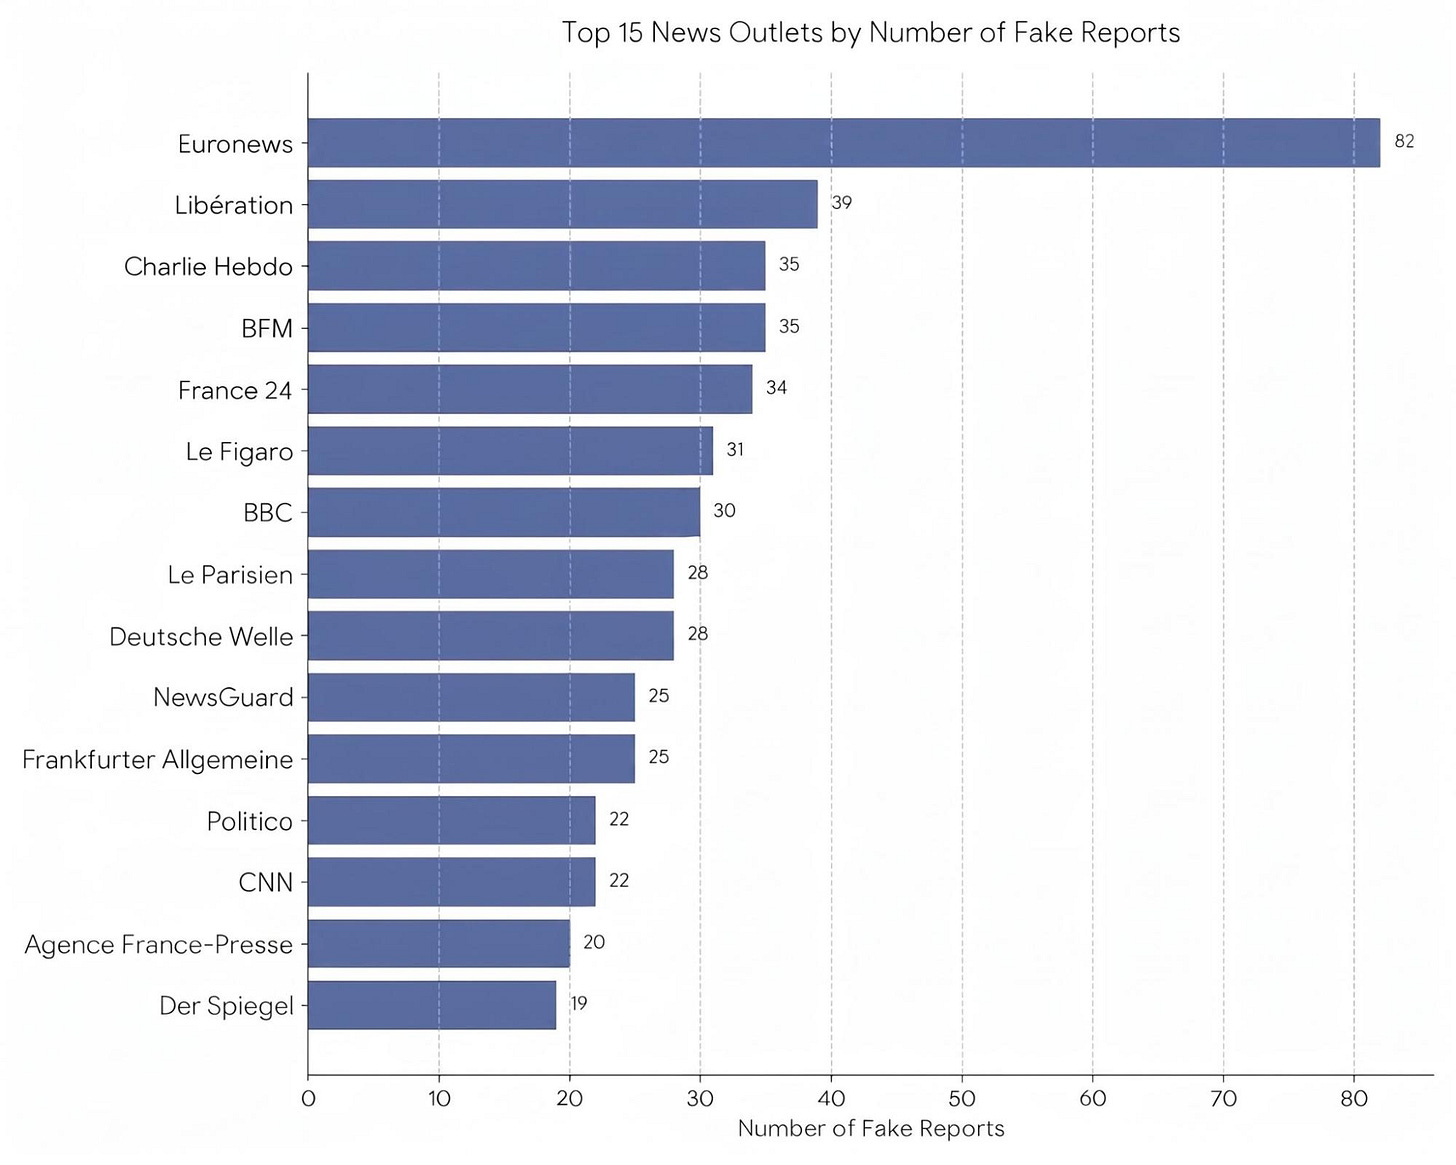
Top news organizations impersonated by Russian influence operation Storm-1516. Source: NewsGuard.
HORIZON THREATS
International activity that may pose a future risk to US homeland security
6. IRANIAN PLOTS TO TARGET AMERICANS ABROAD IN “ADVANCED STAGES”
On October 23, 2026, Director of National Intelligence Jay Clayton sent an unclassified memo to Secretary of State Marco Rubio warning that Iranian efforts to launch lethal attacks on Americans in the Middle East and “certain other countries” had reached “advanced stages” of preparations.
Additional Information:
In recent weeks Iranian officials have repeatedly stated that the country will offer a less restrained and more geographically expansive retaliation against America and its allies in the event of a resumption of hostilities. Supreme Leader Mojtaba Khamenei issued a statement on October 31, 2026, warning of an “immediate and effective response without geographic limitations,” to any major US military operation. Statements by other Iranian officials have implied not only that these attacks could target American officials and businesses in the Middle East but could extend into Europe as well.
7. IRANIAN OPERATIVES LINKED TO SHOOTINGS IN CANADA
An investigation by the Canadian Broadcasting Corporation (CBC) released on October 27, 2026, has found evidence that a dozen shootings targeting Jewish communities, Iranian dissidents, and the US Consulate in Toronto were financed by the Iranian government. The assailants involved in the shootings, mostly in their teens and early twenties, were hired to conduct the shootings through intermediaries on encrypted messaging apps.
Additional Information:
As noted in previous OPFOR Journal Homeland Security Briefs, Iran has used a similar “violence-as-a-service” model of hiring criminals and disaffected young people for acts of vandalism and violence in Europe through encrypted messaging apps in recent months. Local Jewish communities appear to be a major focal point of these attacks in both Canada and Europe.
One of the orchestrators of the Canadian plots, Mohammad Baqer al-Saadi, an Iraqi national and senior official in Kata’ib Hizballah, and an operative of the Islamic Revolutionary Guard Corps (IRGC), was arrested by the FBI in May 2026 on six terrorism-related charges. One of the charges involved an attempt to recruit a Mexican cartel member for an attack on a prominent New York City synagogue in April 2026.
This briefing was compiled by Dan White. Dan is an independent foreign policy analyst based in the New York Metro Area. Dan is a former member of The Wilson Center and The Kennan Institute. Dan holds masters degrees from the Johns Hopkins University School of Advanced International Studies (SAIS), the Naval Postgraduate School, and the University of Washington. Dan is a former officer in the United States Army and a veteran of the War in Afghanistan.
For more information, corrections, or comments, please contact djwhite155@gmail.com.
Names of two arrested Americans: Michael James Bostelle of Pennsylvania and Juan Cecilio Pena Carrillo of Texas.
Names of ten indicted Chinese Nationals: Sun Sheng Ming, Pei Li Guang, Weng Shou Cheng, Han Guo Bin, Wang Jian Jun, Sheng Zhang Kun, Zhang Wei Ping, Zhang Li Ping, Yu Yang, Jin Long.